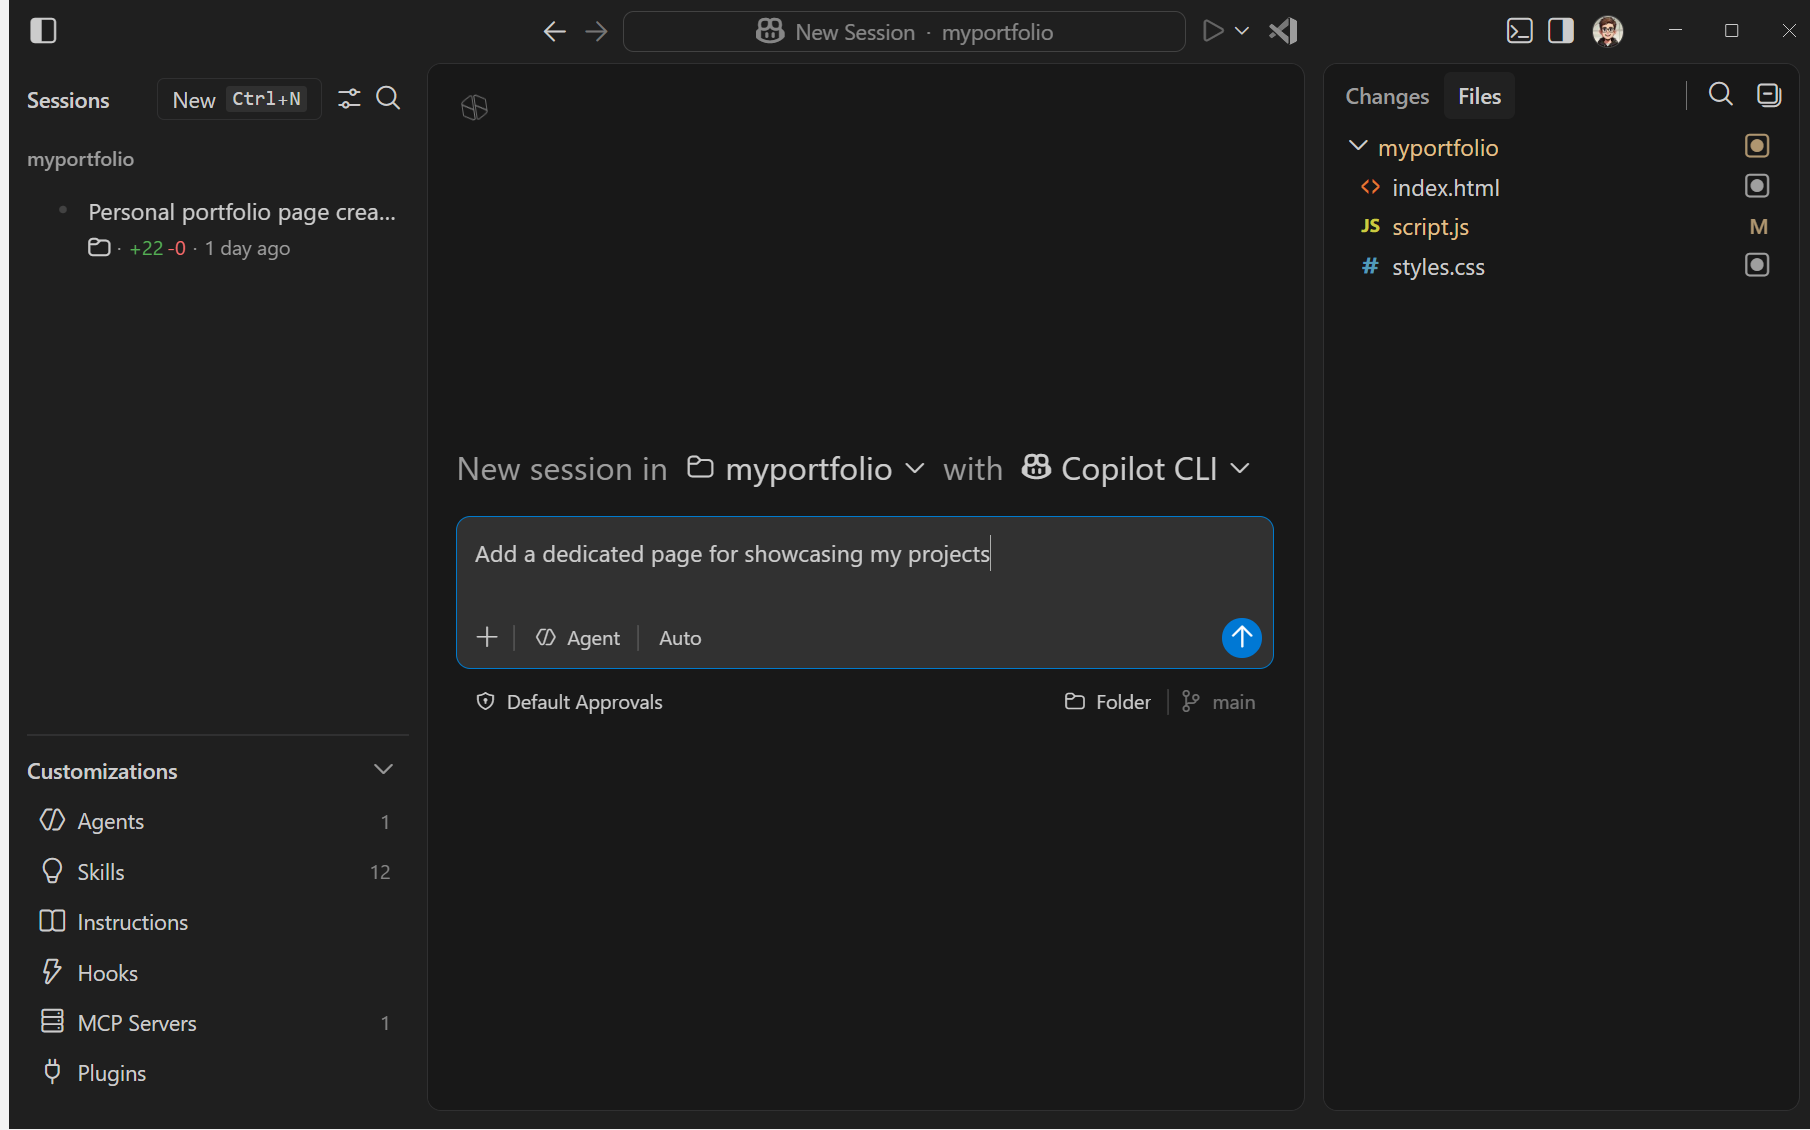
Autonomy is a permission schedule
Grant the authority a task needs, then make escalation visible.
2 min read · Review draft
Reading path / Permissions & safety
A capable model is not a permission system. Separate untrusted context, tool access, credentials and consequential writes.
Prompt injection exploits the moment an agent treats encountered content as authority.
Tool discovery, context retrieval, and account authority need separate review.
Filesystem isolation is only one edge of an agent execution environment.
An agent trace should explain decisions and effects without becoming a second copy of every sensitive input.
Grant the authority a task needs, then make escalation visible.
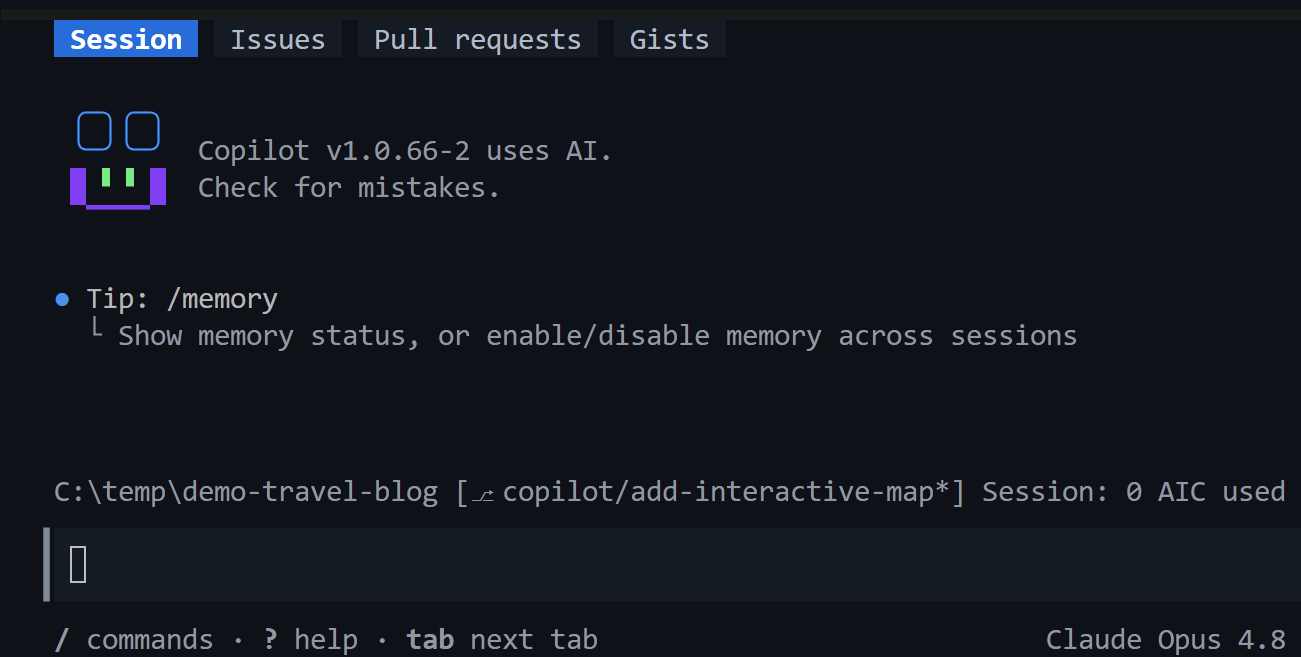
Prompt injection exploits the moment an agent treats encountered content as authority.
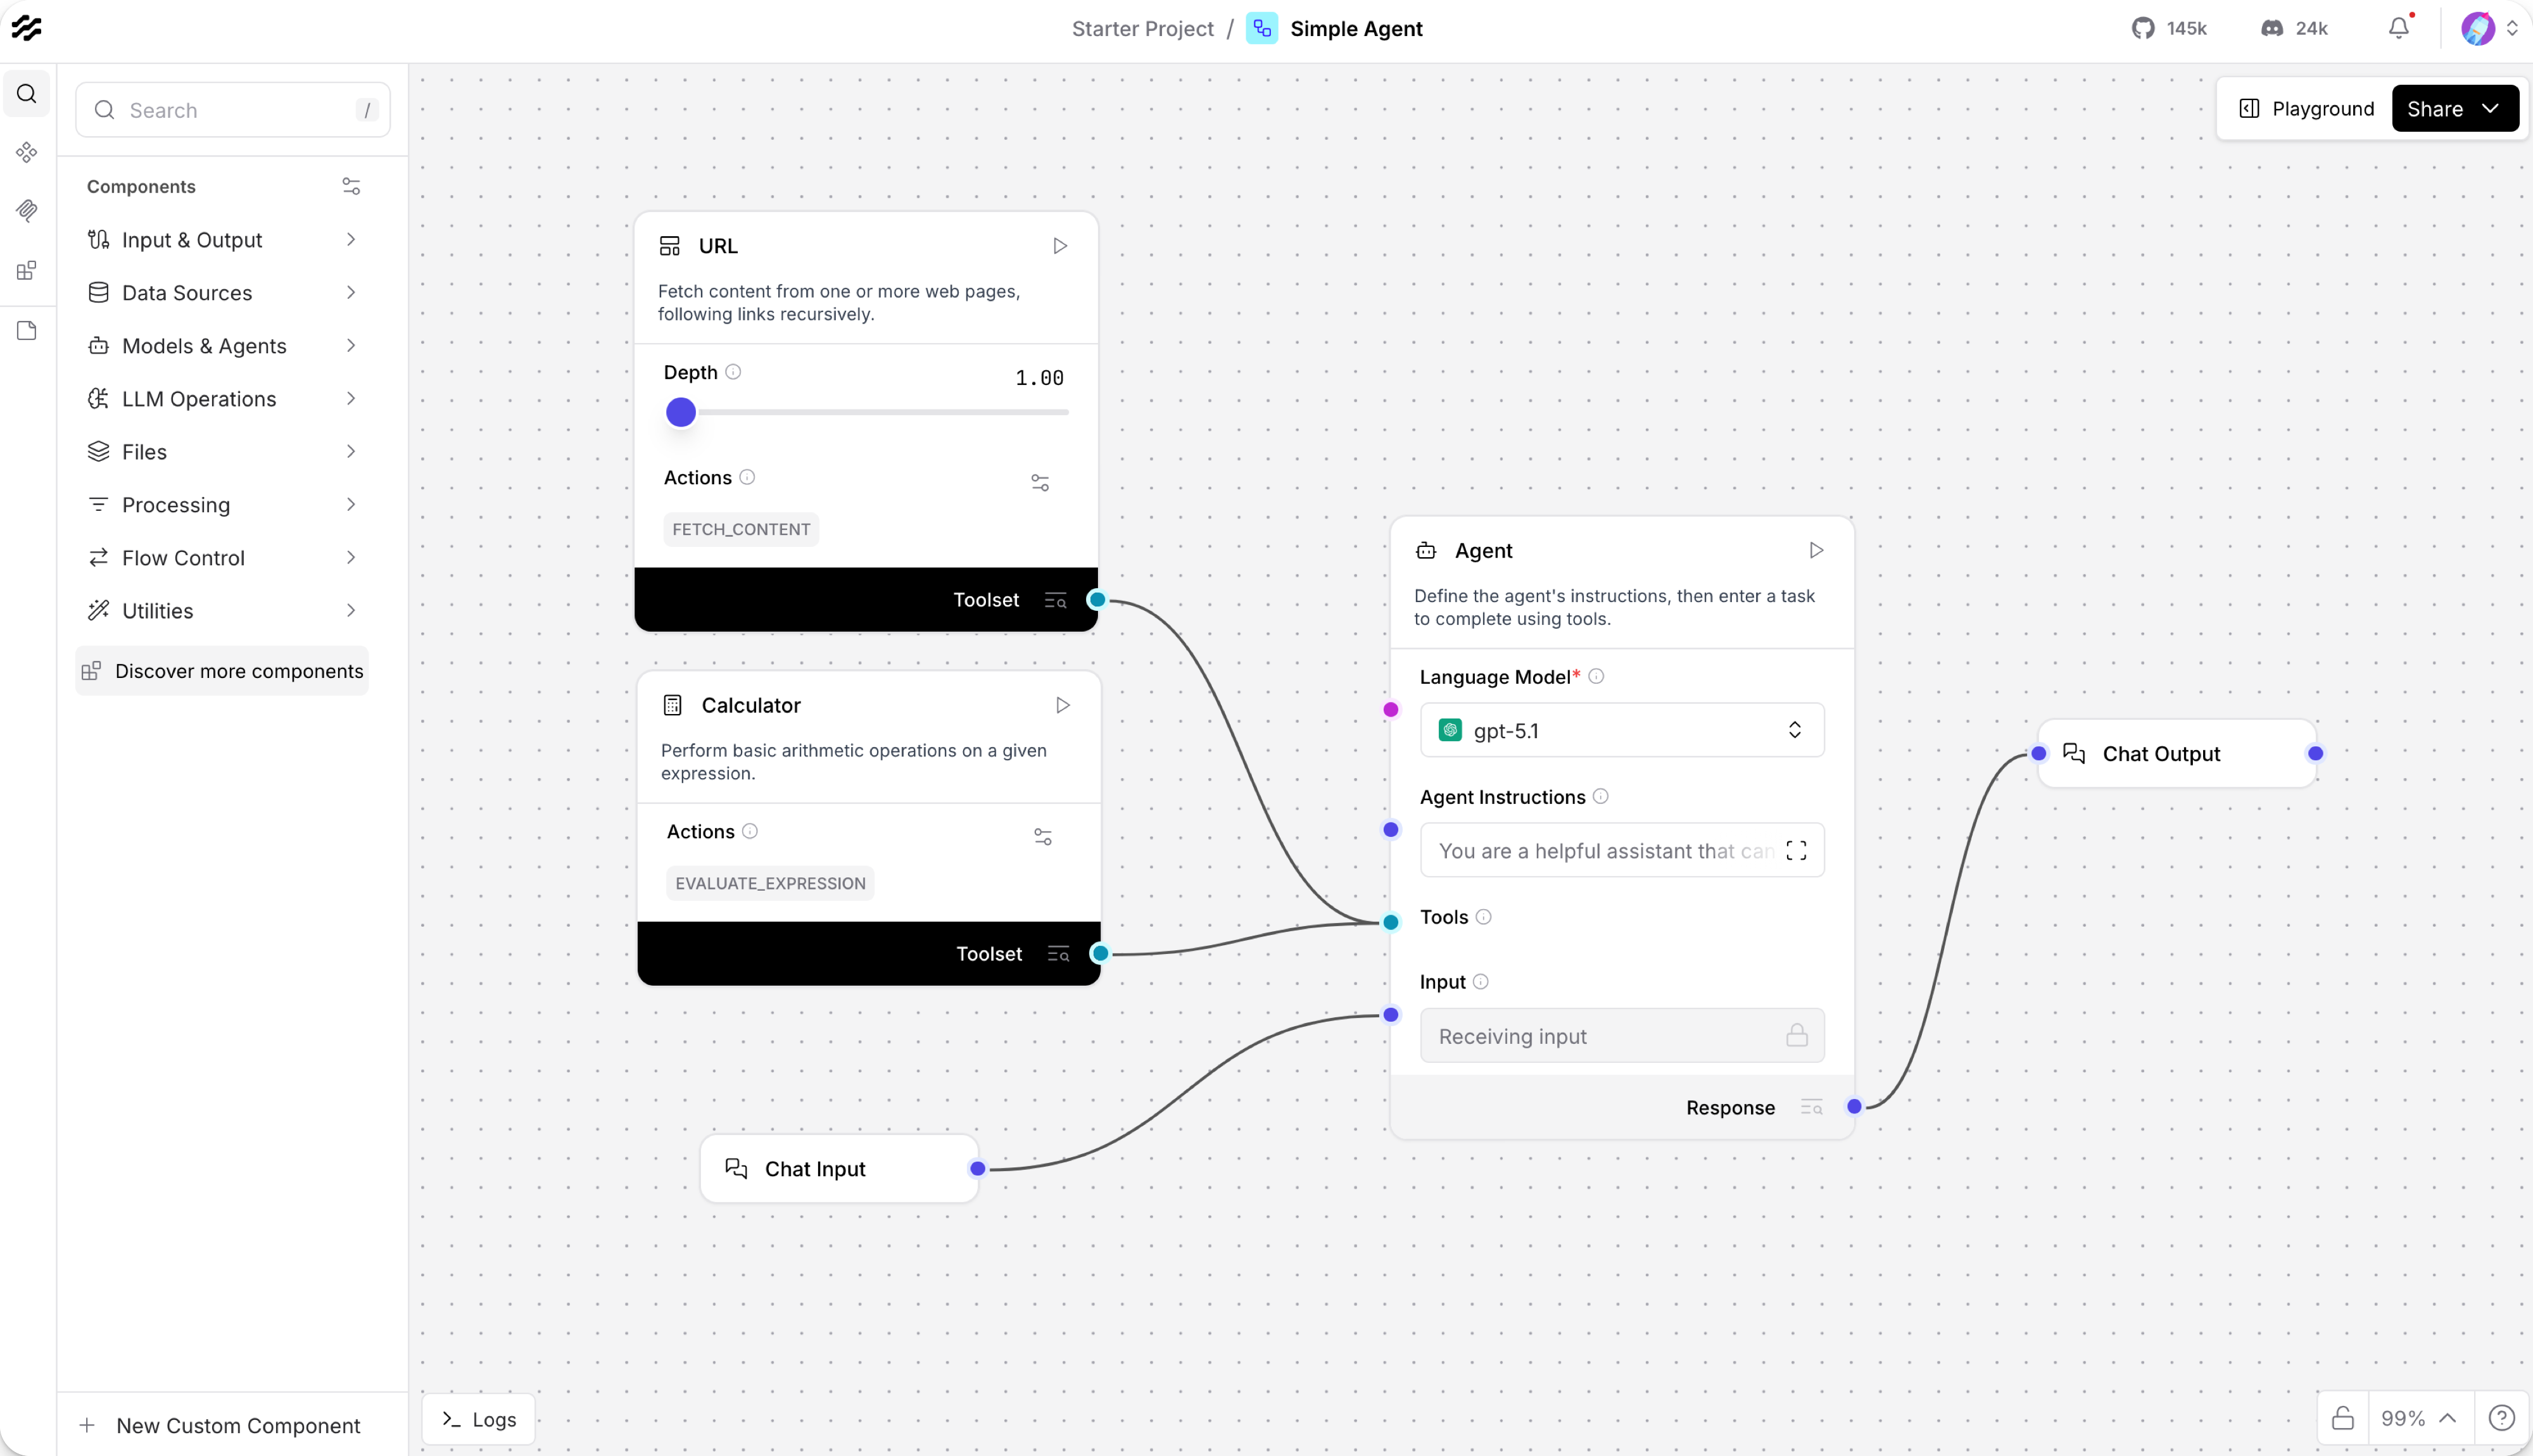
Tool discovery, context retrieval, and account authority need separate review.
Filesystem isolation is only one edge of an agent execution environment.
An agent trace should explain decisions and effects without becoming a second copy of every sensitive input.